A new critical level PHP (which still powers around 75% of the website on internet) vulnerability has been disclosed on 21th October 2026 Wednesday. And this vulnerability is so critical that the hacker doesn’t even need to know the credentials of your server they can launch a attack remotely anywhere and can take control of your website.
Due to this many European Government websites and many MNC websites have been taken down for maintenance.
THE CVE-2026-109618 and CVE-2026-109619 PHP vulnerabilities
These are the code names for the two vulnerabilities that are being found on the PHP the CVE-2026-109618 and the CVE-2026-109619 these two are ranked at 9.8 out of 10 rating on the opencvio.
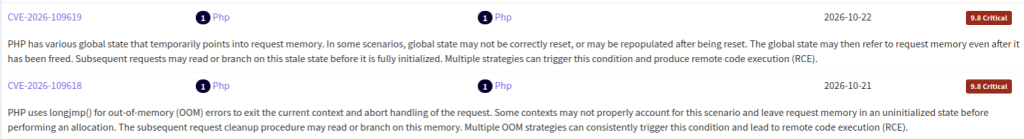
These two vulnerability are in the core of PHP it’s not like you can write safe code and do all the safe practices and can manage to save your website from all these.
How hacker can use this PHP vulnerability to take control of your website
For each task that PHP has been allocated the php spins up a new worker and and when the job finishes the worker cleans up the memory wiping out the slate clean so that other worker can use this memory.
For example if two users fills up the form the php spins up two workers that takes the request and deliver it up to the database.
This is the case in the normal situation but when their are multiple requests and the PHP is not able to handle php triggers a emergency abort function “longjmp()” leaving the memory uncleaned and marking it as a clean the internal pointers pointing to these memory are still their pointing to that exact memory.
From here the hacker can sweep in and can take benefit of this freed memory by doing these three things:
- First sending massive or complex request to the server which can cause to trigger this longjmp() function.
- Then the hacker will send a malicious request to the same php worker which was in charge of serving those complex request. These requests can contains specific request like opening a backdoor.
- And since the stale pointers are still looking on the freed space they get these instructions and start executing it as they where valid instructions.
How to protect your website from this type of attack?
The PHP patch was immediately rolled out by the PHP team and it is for four different versions of version 8 PHP these are 8.5.12, 8.4.27, 8.3.36, and 8.2.35. Make sure to check by using the php -v on your server. If you are running older PHP that 8.2 then the support for these versions has officially ended by the PHP team. However their are some of the third party vendors like the Plesk which have published rebuild PHP version 8.1, 8.0 and 7.4. However it is still recommended to upgrade to the latest version.
If your website is in shared hosting
Then you need to confirm from the provider that they have installed the latest patch.
If you have a VPS
If you have a Linux server then based on the Linux providers seeing that for that particular flavor the patch has been released or not and updating to that mostly the sudo apt update && upgrade will work but in my case running on AWS and having a Amazon Linux for me the process was very different and a very confusing process i say.